What Is Vendor Compliance? A Complete Guide for Manufacturing and Industrial Companies (2026)
Organizations rarely operate alone. Manufacturers, logistics companies, warehouses, engineering firms, construction businesses, and facility-management companies depend on suppliers, contractors, service providers, transporters, and manpower agencies.
These third parties may need to maintain business registrations, statutory records, insurance, safety documentation, contracts, and other requirements throughout their relationship with the organization.
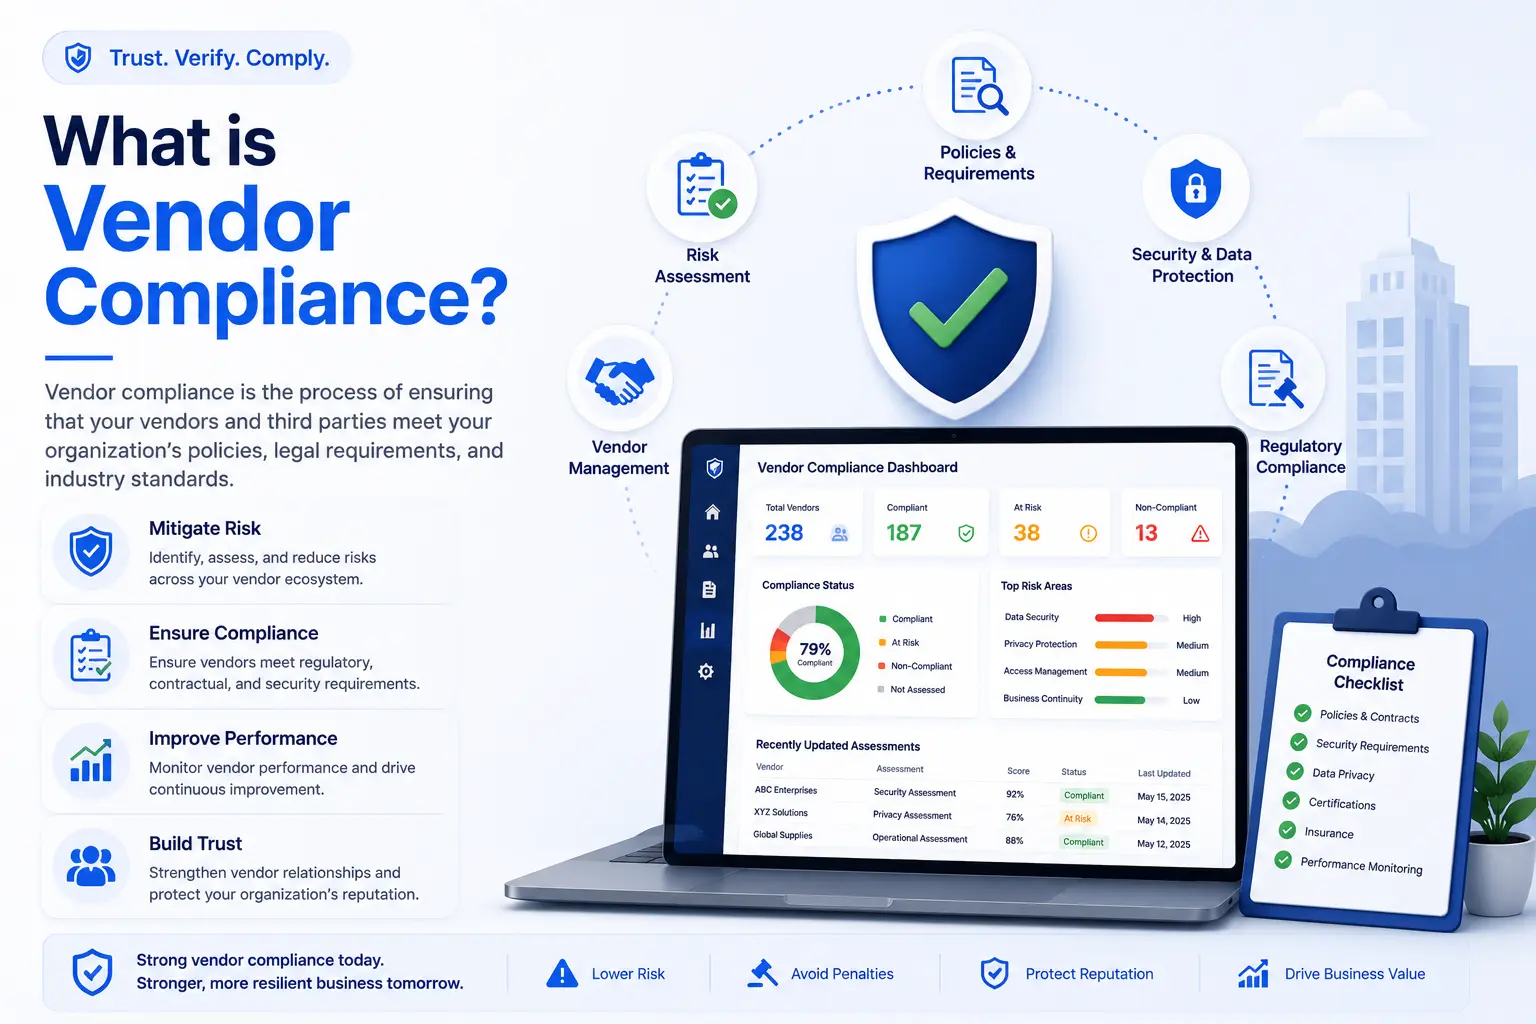
Vendor compliance is the process of ensuring that suppliers, contractors, and other third-party service providers meet the applicable legal, regulatory, contractual, safety, and organizational requirements defined by the company.
Vendor compliance is not simply about collecting documents during onboarding. It is an ongoing process that includes requirements definition, document collection, verification, approval, expiry tracking, renewal, monitoring, reporting, and audit preparation.
This guide explains what vendor compliance means, how the process works, which records organizations commonly manage, and how businesses can build a practical vendor compliance program.
What Is Vendor Compliance?
Vendor compliance is the structured process used to ensure that vendors continue to meet the requirements established by an organization.
These requirements can vary depending on:
- Vendor category
- Services or products provided
- Location
- Industry
- Contractual requirements
- Regulatory obligations
- Operational risk
- Safety requirements
A vendor compliance program may include:
- Vendor registration
- Due diligence
- Document collection
- Document verification
- Approval workflows
- Compliance monitoring
- Expiry tracking
- Renewal reminders
- Corrective actions
- Audit reporting
- Periodic vendor reviews
- Offboarding
The objective is to maintain an accurate and current view of vendor compliance throughout the supplier relationship.
Vendor Compliance vs Vendor Management
Vendor compliance is one part of the broader vendor management process.
Vendor management covers the overall relationship with a supplier, including commercial management, performance, contracts, communication, risk, and compliance.
Vendor compliance focuses specifically on whether the vendor meets defined legal, regulatory, contractual, safety, and organizational requirements.
For example:
| Vendor Management | Vendor Compliance |
|---|---|
| Supplier relationship | Compliance requirements |
| Pricing and contracts | Required documents |
| Delivery performance | Document validity |
| Supplier communication | Statutory records |
| Quality management | Compliance status |
| Business reviews | Audit evidence |
Both functions work together. A supplier may have excellent delivery performance while still having an unresolved compliance issue.
Why Is Vendor Compliance Important?
Vendor compliance helps organizations identify and manage risks associated with external suppliers and contractors.
Without an effective process, organizations may experience:
- Missing vendor documents
- Expired licences or certificates
- Delayed renewals
- Audit observations
- Operational disruptions
- Increased administrative work
- Poor visibility into vendor status
- Difficulty demonstrating compliance
For organizations with many vendors, manually checking every document and following up with every supplier can become difficult to scale.
A structured process provides consistent requirements and clearer ownership.
Who Needs Vendor Compliance?
Vendor compliance is relevant to organizations that depend on external parties, including:
- Suppliers
- Contractors
- Service providers
- Transport vendors
- Manpower agencies
- Maintenance contractors
- Security agencies
- Housekeeping agencies
- Engineering service providers
It is particularly relevant in industries where suppliers or contractors interact with employees, facilities, production operations, customers, or regulated activities.
Common industries include:
- Manufacturing
- Logistics
- Warehousing
- Construction
- Engineering
- Automotive
- Food processing
- Facility management
- Industrial services
What Does Vendor Compliance Include?
A practical vendor compliance program can cover several areas.
1. Business and Registration Information
Organizations may maintain:
- Legal company name
- Registered address
- Contact information
- GST details, where applicable
- PAN details
- MSME information, where applicable
- Bank information
- Vendor category
These details help establish a reliable vendor master record.
2. Statutory and Regulatory Documents
Depending on the vendor and applicable requirements, organizations may collect documents such as:
- GST Registration Certificate
- PAN Card
- PF Registration Certificate
- ESIC Registration Certificate
- Labour or Contractor Licence
- Applicable registrations and certificates
Requirements should be determined based on the vendor’s activities and applicable rules rather than using the same checklist for every vendor.
For a more detailed India-focused checklist, see Vendor Compliance Checklist India.
3. Insurance Documents
Where applicable, organizations may require evidence of insurance coverage such as:
- Workmen compensation insurance
- Public liability insurance
- Other contractually required insurance
The organization should define which policies are required based on the vendor’s activities and risk profile.
4. Safety and Operational Records
For vendors working at industrial sites or facilities, organizations may require records such as:
- Safety training records
- PPE compliance records
- Risk assessments
- Safety procedures
- Other site-specific documentation
These requirements vary by workplace and vendor activity.
5. Periodic Compliance Submissions
Some vendor relationships require recurring submissions rather than one-time documents.
Examples may include:
- Monthly statutory records
- Contribution records
- Attendance records
- Wage or salary records
- Periodic compliance declarations
These recurring requirements need a process for collection, review, and escalation.
See PF and ESIC Vendor Compliance Guide.
The Vendor Compliance Process
A practical vendor compliance process can be organized into the following stages.
Step 1: Define Vendor Requirements
First, determine what each vendor category must provide.
For example, a transport vendor may have different requirements from a housekeeping contractor or an engineering supplier.
Requirements can be based on:
- Vendor category
- Business activity
- Risk level
- Location
- Contract
- Regulatory requirements
Step 2: Register the Vendor
Capture the vendor’s basic business information and create the vendor record.
This provides a foundation for subsequent compliance activities.
Step 3: Collect Required Documents
Request the documents applicable to that vendor.
A vendor self-service portal can allow suppliers and contractors to upload their own records.
See Vendor Self-Service Portal.
Step 4: Verify the Submission
Review documents for:
- Correct document type
- Completeness
- Validity
- Expiry date
- Required information
- Applicable approval requirements
Depending on the organization and document type, verification may be manual, automated, or a combination of both.
Step 5: Approve the Vendor
Relevant teams review the vendor and submitted records.
Depending on the organization, approval may involve:
- Procurement
- Compliance
- HR
- EHS
- Finance
- Plant management
Approval requirements should be defined according to vendor category and risk.
Step 6: Monitor Compliance Continuously
Compliance does not end after approval.
Organizations should monitor:
- Missing documents
- Expiring documents
- Expired documents
- Periodic submissions
- Pending approvals
- Compliance exceptions
Step 7: Send Renewal Reminders
Documents with validity periods should be tracked and renewed before they expire.
Reminder schedules can be configured according to organizational requirements, for example:
- 90 days before expiry
- 60 days before expiry
- 30 days before expiry
- 15 days before expiry
- 7 days before expiry
The appropriate schedule depends on the document and the time required for renewal.
See Vendor Document Expiry Reminder.
Step 8: Review and Report
Compliance teams should periodically review vendor status and generate reports showing:
- Compliant vendors
- Non-compliant vendors
- Missing documents
- Expiring documents
- Expired documents
- Pending approvals
- Outstanding actions
See Vendor Audit Readiness Checklist.
Vendor Compliance Status
A simple status model can make vendor compliance easier to understand.
| Status | Meaning |
|---|---|
| Compliant | Required records are current |
| Pending | Required information or approval is outstanding |
| At Risk | A compliance issue requires attention |
| Expiring Soon | One or more documents are approaching expiry |
| Expired | One or more required documents have expired |
| Non-Compliant | Defined mandatory requirements are not satisfied |
Organizations can customize these statuses to match their internal processes.
Common Challenges With Manual Vendor Compliance
Many organizations still use:
- Excel spreadsheets
- Shared drives
- Paper files
- Calendar reminders
These methods can work for simple processes, but become difficult as the number of vendors and requirements increases.
Missed Expiry Dates
Important documents may expire because renewal dates are not monitored consistently.
Scattered Documents
Vendor records can become distributed across emails, folders, and departments.
Manual Follow-Ups
Compliance teams may spend significant time requesting missing documents.
Human Errors
Manual data entry can result in incorrect dates, duplicate records, or outdated information.
Difficult Audits
Teams may spend considerable time searching for evidence when an audit or inspection occurs.
Limited Visibility
Management may not have a current view of vendor compliance across the organization.
Manual Vendor Compliance vs Automated Compliance
| Manual Process | Automated Compliance Process |
|---|---|
| Excel tracking | Centralized vendor records |
| Email follow-ups | Automated notifications |
| Scattered documents | Central document repository |
| Manual expiry checks | Automated expiry tracking |
| Manual approval tracking | Workflow-based approvals |
| Difficult reporting | Compliance dashboards |
| Time-consuming audits | Faster record retrieval |
| Limited history | Audit trails |
Automation does not eliminate the need for human review. It reduces repetitive work and gives teams better visibility into items that require attention.
Benefits of a Structured Vendor Compliance Program
Reduced Compliance Risk
Organizations can identify missing, expired, or pending requirements earlier.
Better Audit Readiness
Centralized records make it easier to retrieve supporting documentation.
Faster Vendor Onboarding
Standardized requirements and workflows reduce unnecessary back-and-forth.
Improved Visibility
Teams can see vendor compliance status across categories and locations.
Reduced Administrative Work
Automated reminders and workflows reduce repetitive follow-up.
Better Vendor Governance
Consistent requirements improve accountability and standardization.
Stronger Business Continuity
Monitoring critical vendor requirements can help organizations identify issues before they affect operations.
Vendor Compliance Best Practices
1. Define Requirements by Vendor Category
Do not automatically require the same documents from every supplier.
Create requirement sets based on the vendor’s activities and risk.
2. Maintain a Single Vendor Record
Keep important vendor information connected instead of maintaining multiple disconnected spreadsheets.
3. Automate Expiry Tracking
Use automated reminders for documents with validity periods.
4. Assign Clear Ownership
Define who is responsible for collecting, reviewing, approving, and escalating compliance issues.
5. Review Vendors Periodically
Perform regular reviews based on vendor risk and business requirements.
6. Track Exceptions
Record missing documents, expired records, rejected submissions, and corrective actions.
7. Maintain Audit Trails
Keep appropriate history of submissions, approvals, changes, and reviews.
8. Use Risk-Based Controls
High-risk or critical vendors may require stronger due diligence and more frequent monitoring.
Vendor Compliance Checklist
A basic vendor compliance checklist can include:
Vendor Information
- Legal company name
- Address
- Contact details
- Vendor category
- GST details, where applicable
- PAN details
- Vendor risk classification
Documents
- Required registration documents
- Applicable statutory documents
- Applicable insurance documents
- Safety documents, where required
- Contractual documents
Monitoring
- Expiry dates recorded
- Renewal reminders configured
- Missing documents identified
- Periodic submissions monitored
- Compliance exceptions tracked
Governance
- Approval workflow defined
- Compliance owner assigned
- Audit trail maintained
- Periodic review scheduled
- Reports available
For the detailed India-specific checklist, see Vendor Compliance Checklist India.
Vendor Compliance Software: What to Look For
Organizations considering software should evaluate capabilities such as:
- Vendor self-registration
- Vendor self-service portal
- Centralized vendor records
- Document repository
- Configurable document requirements
- Automated expiry reminders
- Approval workflows
- Compliance dashboards
- Audit reports
- Role-based access
- Audit trails
- Document history
- OCR capabilities
- AI-assisted document validation
- Reporting and analytics
- API integration
The right feature set depends on the organization’s size, vendor complexity, existing systems, and compliance requirements.
See Vendor Compliance Software India.
How AI Can Help With Vendor Compliance
AI can assist with document-heavy compliance processes.
Depending on the system, AI can help:
- Extract information from uploaded documents
- Identify document types
- Detect expiry dates
- Validate expected document types
- Flag missing information
- Reduce repetitive data entry
- Prioritize records for human review
AI should support compliance teams rather than replace appropriate human verification and decision-making.
Vendor Compliance and Vendor Lifecycle Management
Vendor compliance is an ongoing part of the vendor lifecycle.
A typical relationship may look like:
Selection → Registration → Onboarding → Compliance → Performance → Risk Monitoring → Renewal → Reassessment → Offboarding
Compliance requirements can change throughout this lifecycle.
For a broader view of the complete supplier journey, see Vendor Lifecycle Management.
How VendorCompliancePro Helps
VendorCompliancePro is designed to help organizations manage vendor compliance from a centralized platform.
Capabilities include:
- Vendor self-service portal
- Vendor registration
- Centralized vendor records
- Document repository
- Configurable document requirements
- AI-powered document validation
- OCR processing
- Approval workflows
- Automated expiry reminders
- Compliance dashboards
- Vendor risk monitoring
- Audit trails
- Reports and analytics
These capabilities help organizations reduce manual follow-ups, improve compliance visibility, and maintain organized vendor records throughout the vendor relationship.
Frequently Asked Questions
What is vendor compliance?
Vendor compliance is the process of ensuring that suppliers, contractors, and other third parties meet applicable legal, regulatory, contractual, safety, and organizational requirements.
Why is vendor compliance important?
It helps organizations identify compliance gaps, improve vendor visibility, support audits, and reduce risks associated with external suppliers and contractors.
What documents are commonly collected from vendors?
Requirements vary by vendor category. Common examples include GST registration, PAN, PF and ESIC records, applicable labour licences, insurance documents, safety records, and contractual documents.
Is vendor compliance only about documents?
No. Documents are an important part of vendor compliance, but the process can also include approvals, periodic submissions, risk controls, audits, corrective actions, and ongoing monitoring.
How often should vendor compliance be reviewed?
Review frequency should depend on the vendor’s risk, business criticality, document requirements, and organizational policies. High-risk vendors may require more frequent reviews.
Can Excel be used for vendor compliance?
Excel can be suitable for small and simple vendor populations. As requirements and vendor counts increase, dedicated software can provide stronger automation, workflows, visibility, and audit history.
What is the difference between vendor compliance and vendor risk management?
Vendor compliance focuses on meeting defined requirements. Vendor risk management is broader and evaluates potential risks associated with the vendor, including operational, financial, cybersecurity, quality, and compliance risks.
Can vendor compliance be automated?
Yes. Organizations can automate activities such as vendor registration, document collection, approval workflows, expiry reminders, reporting, and compliance monitoring.
Conclusion
Vendor compliance is an ongoing business process, not simply a document-collection exercise.
A strong vendor compliance program connects requirements, onboarding, document verification, approvals, expiry tracking, monitoring, reporting, and periodic review.
Organizations that replace fragmented spreadsheets and email-based processes with structured workflows can improve visibility, reduce repetitive administrative work, and stay better prepared for audits.
For manufacturing and industrial companies, the most effective approach is to make vendor compliance part of the complete supplier lifecycle — from onboarding through ongoing monitoring, renewal, reassessment, and offboarding.